
When you invest in software, you do not pay only for features. You pay for every future change, every bug fix, every deployment, every security update, and every hour your team spends understanding the system. That is why code quality is not a technical luxury. It is a business cost driver.
At SKM Group, we see this pattern often. A product may look stable from the outside, but under the surface, weak structure, unclear logic, and unmanaged technical debt quietly increase delivery costs. You notice it when simple changes take too long. You feel it when releases become risky. You pay for it when infrastructure grows faster than revenue.
Code quality describes how easy, safe, and cost-effective software is to understand, change, test, scale, and maintain. For you as a decision-maker, it means fewer surprises. Better planning. Lower operational risk. Faster delivery without constant firefighting.
A clean codebase gives your business flexibility. A poor one turns every new feature into negotiation with the past.
Code quality definition and core software engineering principles
In software engineering, quality starts with clarity. Code should express business logic in a simple, consistent, and testable way. It should follow principles such as separation of concerns, low coupling, high cohesion, secure design, and predictable architecture.
These principles reduce dependency chaos. They also help new developers join a project faster, which matters when you scale a team through IT outsourcing or extend an internal department with external specialists.
Technical attributes that define high-quality source code
High-quality source code is readable, modular, tested, secure, observable, and documented where needed. It avoids unnecessary complexity. It uses clear naming. It keeps business rules visible instead of hiding them inside fragile technical shortcuts.
For your company, this means one thing. The system is easier to change without breaking what already works.
Why code quality directly influences operational costs
Poor code increases the cost of every action. Developers need more time to understand dependencies. Testers face more regressions. DevOps teams handle unstable releases. Business teams wait longer for improvements.
Good code quality lowers these costs because changes become smaller, safer, and more predictable.
Common indicators of poor code quality in enterprise systems
You may not read the code, but you can see the symptoms. Long delivery cycles. Frequent production bugs. Releases postponed because “something unexpected came up.” High developer turnover. Expensive onboarding. Fear of touching old modules.
When these signs repeat, the problem is rarely one developer. It is usually the system’s internal structure.
The relationship between maintainability, scalability, and business performance
Maintainability protects your budget. Scalability protects your growth. When both are weak, your product becomes expensive exactly when the business needs speed.
A maintainable system lets you add features without rewriting half the platform. A scalable system supports more users, more data, and more integrations without wasteful infrastructure spending.
How code quality management supports long-term software reliability
Code quality management is the discipline of keeping software healthy over time. It combines standards, reviews, automated tests, architectural control, and regular technical debt decisions.
At SKM Group, we treat it as part of responsible product ownership. Not as a one-time cleanup. As an ongoing business practice.
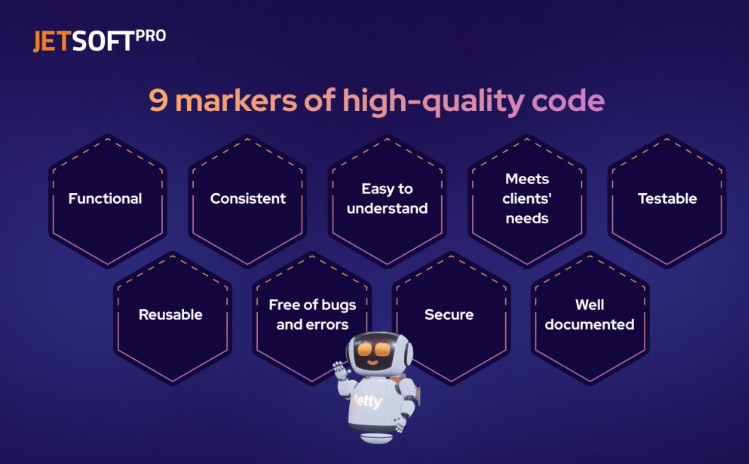
You cannot improve what you do not measure. A strong code quality kpi framework helps your team connect engineering health with business impact. The goal is not to collect vanity metrics. The goal is to identify where cost, risk, and delay are forming.
Code quality kpi for maintainability and technical debt
Maintainability KPIs show whether your system is becoming easier or harder to change. Technical debt metrics show where shortcuts are accumulating. Together, they help you decide whether to refactor, modernize, or rebuild selected components.
Cyclomatic complexity and cognitive complexity metrics
Cyclomatic complexity measures how many execution paths exist in code. Cognitive complexity shows how hard logic is for humans to understand. High values usually mean slower debugging, higher risk, and more expensive maintenance.
Code coverage, defect density, and reliability indicators
Code coverage shows how much code is tested, but it must be read carefully. High coverage does not always mean strong tests. Defect density, production incident trends, and escaped bugs give a more practical picture of reliability.
Mean time to recovery (MTTR) and deployment frequency
MTTR tells you how quickly your team restores service after failure. Deployment frequency shows how often value reaches users. Healthy teams usually recover faster and release more often because their systems are easier to control.
Maintainability index and code churn analysis
Maintainability index combines several signals into one technical health score. Code churn shows how often parts of the system change. When churn is high in poorly structured modules, cost risk grows quickly.
Engineering KPIs that support business cost optimization
The most useful engineering KPIs connect technical work with financial outcomes:
Bad code creates hidden tax. Every new feature requires extra analysis. Every bug fix may trigger another bug. Every release needs more manual checks. Over time, your team stops building momentum and starts defending the system from itself.
Infrastructure costs also rise. Inefficient queries, duplicated services, memory leaks, poor caching, and uncontrolled background jobs force you to buy more cloud resources than the business really needs. This is why technical debt is not only a developer issue. It appears later as higher hosting bills, slower delivery, and weaker customer experience.
If you want to avoid this pattern, a strong software development checklist helps align requirements, architecture, testing, security, and delivery before costs become permanent.
Code climate quality refers to the overall technical health environment of a software project. It includes maintainability, test coverage, duplication, complexity, security issues, and team habits around code review.
The real value is visibility. When your team sees where risk is growing, it can act early. Instead of waiting for a major incident, engineers can improve modules gradually. For you, this means fewer emergency rewrites and more stable planning.
Code quality analysis is the process of examining source code, architecture, dependencies, tests, and runtime behavior to detect weaknesses before they become business problems.
Static code quality analysis for early defect detection
Static analysis checks code without running it. It detects style issues, unsafe patterns, duplicated logic, unused code, dependency risks, and some security vulnerabilities. It is fast, repeatable, and ideal for early feedback.
Dynamic code analysis during runtime validation
Dynamic analysis observes software while it runs. It helps detect memory problems, performance bottlenecks, race conditions, API failures, and behavior that static tools cannot fully understand.
Software architecture analysis and dependency evaluation
Architecture analysis shows whether system boundaries are clear. It checks dependencies, service communication, data flow, and module responsibility. This is especially important in enterprise systems where one weak dependency can slow the entire platform.
Technical debt identification through code analysis
Technical debt becomes expensive when nobody tracks it. Analysis helps identify debt by severity, business impact, and repair effort. This allows your team to fix the most expensive issues first.
Automated quality gates within CI/CD pipelines
Quality gates stop risky code before it enters production. They can check tests, coverage, security, complexity, and code style. Combined with DevOps automation, they help your team release faster and safer.
Using analysis results to prioritize refactoring activities
Not every issue deserves immediate action. Good teams prioritize refactoring where it protects revenue, supports upcoming features, or reduces incident risk. This is where engineering judgment matters more than tool reports.
Code quality scanning automates inspection across the software development lifecycle. It should happen during pull requests, builds, security checks, and release preparation.
Scanning gives your team continuous feedback. It reduces manual review pressure and catches repeated mistakes. It also supports compliance, especially when your software handles sensitive data, payments, or regulated workflows.
In our work at SKM Group, automation is often a key part of custom software development, because modern systems must be delivered quickly without losing control over reliability.
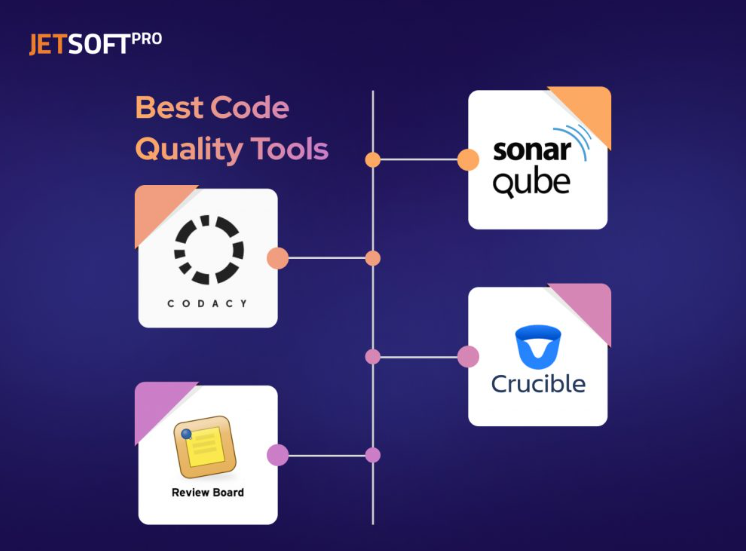
Choosing code quality software is not about buying the most complex platform. It is about matching tools to your engineering maturity, technology stack, security needs, and delivery model.
Common solutions include static analyzers, test coverage tools, dependency scanners, security scanners, observability platforms, and code review systems. The best setup is integrated into daily work. Developers should receive feedback where they already work, not in a separate report nobody reads.
If you cooperate with a software outsourcing provider, tool consistency becomes even more important. Shared standards reduce communication gaps and make delivery easier to verify.
Code quality improvement should be practical. You do not need to stop product development for months. You need a clear process that reduces risk step by step.
Refactoring legacy systems without business disruption
Legacy refactoring should be incremental. Start with the most expensive modules, add tests around critical flows, and improve structure before adding major features. This protects continuity while reducing long-term cost.
Establishing secure coding standards across teams
Secure coding standards reduce vulnerability risk and make expectations clear. They should cover authentication, authorization, input validation, secrets management, logging, dependencies, and data protection.
Integrating automated testing into continuous integration
Automated tests give confidence during change. Unit tests protect logic. Integration tests protect communication. End-to-end tests protect user journeys. Together, they lower regression risk and support faster delivery.
Continuous code quality scanning for faster release cycles
Continuous scanning shortens feedback loops. Developers see issues early, fix them faster, and avoid costly late-stage corrections. This improves release confidence and supports more predictable product planning.
Implementing effective code quality management processes
Processes must be simple enough to survive real project pressure. Code reviews, architecture checks, Definition of Done, quality gates, and debt reviews should be part of normal delivery, not extra bureaucracy.
Supporting digital transformation through legacy software modernization and custom software development services
Digital transformation often fails when old systems cannot support new business models. Legacy modernization, API redesign, cloud optimization, and new product modules can turn technical limits into growth capacity.
That is why SKM Group combines IT services with engineering standards, modernization experience, and practical delivery. Our case study on streamlining sports camp bookings shows how better software structure can support smoother operations and better customer experience.
Code quality affects cost because it affects everything after the first release. Maintenance. Scaling. Security. Hiring. Delivery speed. User trust. Infrastructure. Risk.
When you ignore quality, software becomes harder to change and more expensive to operate. When you manage it, your technology becomes a business asset instead of a hidden liability.
At SKM Group, we believe quality is not about perfect code. It is about software that helps you move faster without creating future damage. That is the difference between short-term delivery and sustainable growth.
Check also:

Code quality means software is readable, maintainable, secure, testable, and ready for change. It matters because poor structure increases development cost, slows releases, and raises operational risk.
Teams should monitor complexity, test coverage, defect density, code churn, MTTR, deployment frequency, maintainability index, and technical debt trends. A useful code quality kpi must connect engineering signals with business cost.
Code quality analysis is the broader evaluation of code, architecture, dependencies, tests, and technical debt. Code quality scanning is the automated inspection process that runs throughout development.
Code climate quality improves maintainability by showing where complexity, duplication, low coverage, and risky dependencies are growing. This helps your team fix problems before they slow delivery.

In our team, Dominik Bigosiński is responsible for driving the growth of online businesses through the strategic use of content. As an expert in his field, he has collaborated with organizations from the US, UK, Norway, and Poland since 2018, contributing to the development of over 100 blogs and supporting more than 450 B2B and e-commerce brands worldwide. His passion for conscious personal growth and philosophy is reflected in his work, where he focuses on delivering thoughtful, audience-centered strategies that drive long-term results.
Need tailor-made software? We build scalable, secure solutions from scratch.
Discover moreStrategic insights into technology, software development, and digital growth
Modern engineering teams are under constant pressure. They are expected to deliver faster, maintain reliable systems, operate in secure cloud environments, and achieve predictable outcomes.
Business application development is not only about writing code. It is about making the right decisions before code becomes expensive. At SKM Group, we use product roadmapping to help you turn business goals, system limits, user needs, and technology
When you invest in software, you do not pay only for features. You pay for every future change, every bug fix, every deployment, every security update, and every hour your team spends understanding the system.
When you invest in software, you are making a long-term decision that goes far beyond the initial release. The real challenge begins when your system needs to evolve—when new features are added, integrations are expanded, and existing components must
Poor data architecture does not always break your business systems at once. More often, it creates quiet damage: inconsistent reports, duplicated records, unclear KPIs, and decisions based on numbers nobody fully trusts.
Software complexity rarely appears overnight. It grows quietly with every shortcut, integration, legacy module, and undocumented business rule. At SKM Group, we see how this hidden technical weight can turn even a strong product roadmap into a slow
Your company may have many good tools. But good tools do not guarantee good communication. When business systems stop sharing data clearly, everyday work becomes slower, riskier, and harder to manage.
Every business-critical system has a second life after deployment. That life is shaped by updates, fixes, monitoring, documentation, and technical decisions that are easy to postpone.
At first, manual workflows, disconnected systems, and spreadsheets may seem manageable. But when your company begins serving more customers, processing more data, and managing more complexity, operational inefficiencies become impossible to ignore.
Modern enterprises need more than generic software subscriptions. As operations grow more complex, companies require digital infrastructure that supports automation, scalability, cybersecurity, advanced integrations, and real-time operational visibil
Modern automotive performance is no longer built only in the garage. It is built in software. Today’s vehicles rely on complex ECUs, communication protocols, telemetry systems, and real-time diagnostics that require far more than traditional mechanic
Modern companies no longer struggle with a lack of software. They struggle with too many disconnected tools, fragmented workflows, and operational processes that were never designed to work together efficiently.

If you are making decisions about modern software delivery, you will inevitably ask yourself: what is azure DevOps and why does it matter for your business? At SKM Group, we see it not as a tool, but as a structured ecosystem that connects.
When you invest in custom software, you are not just buying code—you are buying speed, reliability, and confidence. At SKM Group, we rely on DevOps tools as the backbone of that promise.
When you ask what is DevOps engineer, you are really asking about one of the most critical roles in modern software delivery. At SKM Group, we see a DevOps engineer not as a single function, but as a connector of systems, teams, and outcomes.
At SKM Group, you don’t just buy software—you invest in a process that determines whether your product succeeds or quietly fails in the background. One of the most transformative approaches shaping modern software delivery is DevOps.
You have heard the promise. Faster systems. Lower costs. Infinite scale. The cloud as a cure for every architectural weakness accumulated over twenty years of digital growth. And yet, from our experience at SKM Group, we have seen the opposite happen
At SKM Group, we meet organizations every week that still rely on infrastructure designed fifteen or twenty years ago. It runs. It supports operations. It feels stable. But beneath that surface, the architecture quietly expands your cybersecurity exp
Legacy systems rarely fail loudly. They age quietly. They grow around your organization like concrete poured decades ago – solid, load-bearing, but rigid. When documentation disappears, original developers leave, and integration requirements multiply
If you are responsible for technology decisions in your organization, you have probably heard both terms used almost interchangeably. Technical debt. Legacy systems. Obsolete platforms.
When you hear lean software development meaning, you should not think about a trendy buzzword. You should think about engineering discipline designed to remove friction from value delivery.
When you invest in software, you are not just buying code. You are buying speed, predictability, flexibility, and the ability to react to market change. At SKM Group, we see software as a living system, not a finished product frozen in time.
At SKM Group, we often see decision-makers pause at one deceptively simple question: what is a software development kit, and why does it matter so much to the success, cost, and scalability of your digital product?
From the perspective of SKM Group, when you ask what a mobile apps application really is, you are not asking a marketing question. You are asking an engineering question with direct business consequences.
At SKM Group, we see software resilience as the living backbone of modern digital ecosystems. It is the capability of your systems to absorb shocks, maintain essential functions, and recover faster than your business stakeholders expect.
As SKM Group, we often see that companies underestimate how deeply software dependency structures shape the long-term health of their digital products. You might assume dependencies “just work in the background,”
As SKM Group, we see every day how leaders like you face a rising paradox: you’re expected to innovate faster than ever, yet every new system you adopt must now prove its financial value with absolute clarity.
Technology doesn’t wait. Neither should you. Every software environment that powers your operations today will either evolve—or become obsolete. That’s the simple reality of digital transformation.
You’ve probably heard it before – “Customer is king.” But in 2025, that phrase isn’t just a cliché. It’s the operational truth that defines which businesses thrive and which fade into the noise.
Every industry, from manufacturing to finance, now depends on intelligent software products that enhance performance, streamline workflows, and enable long-term scalability.

When you think about the cloud, you probably imagine endless virtual servers humming somewhere in the background, waiting to process your business logic. But here’s the thing—you no longer have to.
Digital transformation isn’t a buzzword anymore—it’s your reality. You already know that running your business on outdated systems slows down growth, frustrates employees, and makes customers leave for competitors who can deliver faster.

When you sit down to plan your next digital product, one of the first questions that arises is: which app development frameworks will actually get you there?
The digital race is not about speed alone—it’s about precision, resilience, and the ability to deliver value faster than your competitors. As decision-makers in technology, you know the stakes are high.
When you build software, you’re not just creating a product—you’re making a promise. A promise that it will work as intended, delight its users, and deliver measurable value. But promises in software are fragile.
You’ve seen the term software scalability meaning pop up everywhere lately. But what does it really mean for your business—not just for developers? At SKM Group, we define scalability.
You know your business. You know your customers. But in today’s digital-first market, knowing isn’t enough – acting fast, adapting to trends, and delivering personalized experiences is what separates market leaders from followers
If you’re searching for ways to streamline complex builds or accelerate your software roadmap, specialized outsourcing is a smart direction. By leveraging Application Development Outsourcing or SaaS Development Outsourcing, you gain rapid access.
Your business runs on technology, whether you notice it daily or not. Choosing the right IT services shapes everything from operational resilience to your capacity for innovation.

If you're leading a business today, you're likely balancing innovation with efficiency, speed with precision, and growth with risk. That’s where specialized software outsourcing services step in — not just as a cost-saving tool, but as a strategic.

Software development processes best practices aren't just buzzwords—they are critical frameworks that shape how successful products come to life. As someone making decisions about technology investments

At SKM Group, we believe that truly successful software starts with a deep understanding of Software Engineering and Design—not just as a process, but as a discipline that brings structure
At SKM Group, we believe clarity is the cornerstone of successful software delivery. If you're navigating digital transformation or evaluating software partners, understanding what is software development methodology

For decision-makers managing IT outsourcing or legacy modernization, choosing between Agile and Waterfall is a financial and strategic decision. This guide explores how iterative implementation minimizes risk and accelerates ROI in distributed teams.
The ability to build a high-performance outsourcing development team can dramatically accelerate product delivery while reducing operational overhead. But to do it right, you need more than just a vendor
Offshore outsourcing software development has evolved from a cost-saving tactic into a strategic pillar for tech-driven organizations. When executed properly, it empowers you to scale faster, access niche expertise, and accelerate time-to-market with

Technology is the backbone of modern business. Whether you're a startup or an enterprise, your IT infrastructure determines how efficiently you operate, how well you serve customers, and how secure your data remains. Choosing the right IT service pro

The software development process is a structured approach to creating software, ensuring efficiency, quality, and alignment with user needs. It encompasses a series of stages, from gathering requirements to maintaining the final product.
Choosing the right business software development partner is one of the crucial decisions that might shape your company's future. With so many choices for enterprise software development companies, how will you go about making the right choice?
Choosing the right partner for your software project is a critical decision. Should you hire an individual custom software developer or collaborate with a full-fledged software development company?

Customized software solutions are the answer for companies that want to streamline operations, optimize workflows, and stay ahead. Here at SKM Group, we understand your need for tailored solutions that align with your unique goals.

Investing in custom software development can feel like navigating uncharted waters. As a decision-maker, you might wonder how custom software development costs against off-the-shelf alternatives, or whether it’s worth pursuing.
IT projects often run over budget or take too long. Agile changes that by delivering value quickly, adapting to evolving needs, and giving leaders control over costs and ROI, helping businesses stay competitive and responsive.

When embarking on a new software project, you're faced with a crucial question: will this idea work? You don’t want to spend months on development only to discover that a critical assumption was wrong.

If you've ever wondered how to create an app, you're not alone. Many businesses are seeking ways to expand their digital footprint, and a dedicated app can be a powerful tool to achieve just that.

Creating a mobile application is complex, and understanding the development cost is crucial for any business aiming to launch a successful app. With costs influenced by numerous variables, knowing what affects your budget and where your money goes

Having a clear, structured approach is essential. Whether you're diving into your first project or overseeing a complex, custom build, the journey can feel overwhelming.
Understanding what is a software life cycle is crucial. The term encapsulates every phase a software product goes through, from inception to retirement. At SKM Group, when you understand this life cycle deeply.

Encountering technical problems is inevitable in our tech-driven lives. This article outlines basic steps to troubleshoot common issues like internet connectivity, software bugs, and peripheral device problems.

Comments